ENTERTAINMENT · STAFF CORRESPONDENT
Delhi-NCR NBFCs Hit by Rs 105 Crore Cyber Fraud, Investigators Detect Use of AI Tools
Cybercriminals have allegedly siphoned off more than Rs 105 crore from non-banking financial companies (NBFCs) across Delhi-NCR by exploiting weaknesses in their digital systems and redirecting approved loan payments into fraudulent bank accounts. The investigation has also uncovered indications that artificial intelligence tools were used to automate parts of the attacks and make it harder to trace the perpetrators.
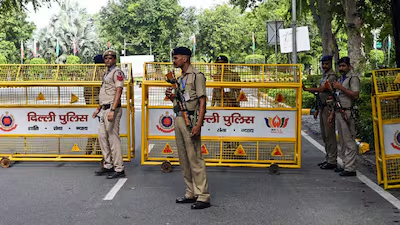
Delhi Police have arrested 20 people in connection with the cases, while investigators have traced and frozen portions of the stolen money. The operation has raised concerns about cybersecurity at financial institutions, particularly smaller lenders that may lack adequate protection against increasingly sophisticated digital attacks.
The fraud cases form part of a wider pattern of cyberattacks targeting NBFCs across India, with financial institutions reporting losses running into hundreds of crores of rupees.
How the Rs 105 Crore Fraud Was Carried Out
Investigators say the alleged fraudsters targeted vulnerabilities in the software systems used by NBFCs to process loan applications and disburse funds.
Rather than relying on conventional scams that trick individual customers into transferring money, the attackers allegedly gained unauthorised access to financial companies’ systems. They then identified loans that had already been approved but had not yet been paid to the intended borrowers.
The criminals allegedly manipulated payment instructions to redirect the money into accounts controlled by accomplices, commonly known as mule accounts. These accounts can be used to receive illicit funds before they are withdrawn, transferred elsewhere or converted into cryptocurrency.
Police investigations indicate that the attackers exploited weaknesses in publicly accessible applications and software interfaces. In some cases, they allegedly used cloud servers whose internet protocol addresses had already been approved by the targeted companies’ security systems.
This allowed fraudulent requests to resemble legitimate transactions, potentially enabling them to bypass certain security checks.
AI Tools Allegedly Helped Automate Attacks
One of the most concerning aspects of the investigation is the reported use of artificial intelligence to speed up cyberattacks.
Investigators have identified indications that AI-assisted tools were used to generate or execute commands against vulnerable financial systems. In one earlier case involving an NBFC, police reportedly found that a Chinese AI platform called CyberStrikeAI had been used to send command scripts.
The suspected use of such tools suggests that criminals may be automating tasks that would otherwise require substantial technical expertise. Automation can allow attackers to exploit weaknesses more quickly, process numerous transactions and operate across multiple systems in a short period.
However, the involvement of AI does not necessarily mean that every stage of the fraud was automated. Investigators are still examining the methods used in individual cases and the extent to which artificial intelligence contributed to the attacks.
Police Arrest 20 Suspects, Recover Part of the Money
Delhi Police have arrested 20 people in cases involving affected NBFCs in the National Capital Region. Earlier reporting on the investigation indicated that approximately Rs 18 crore had been detected and seized from the more than Rs 65 crore lost by 12 NBFCs in the region.
A subsequent report put the wider loss figure at approximately Rs 105.67 crore across at least 14 NBFCs, with around Rs 19.12 crore traced and placed under a lien. These figures relate to different stages and scopes of the investigation and may change as additional complaints are examined.
Investigators are working to establish the roles of suspected hackers, account holders and other individuals allegedly involved in moving the money. They are also attempting to identify additional accounts and recover funds before they can be withdrawn or transferred beyond the reach of authorities.
Why Smaller Financial Companies Are Vulnerable
Police officials have warned that gaps in cybersecurity systems can make smaller NBFCs particularly attractive targets.
Some companies reportedly use software with inadequate protection for internet-facing applications, outdated interfaces or insufficient safeguards around payment credentials. If attackers gain access to these systems, they may be able to manipulate disbursement instructions without triggering the usual checks.
Delayed reconciliation of accounts can make matters worse. If a company reviews its transactions only after several days, unauthorised transfers may remain undetected until the money has already moved through multiple accounts.
Authorities have urged financial institutions to conduct security audits, strengthen authentication controls and follow cybersecurity advisories issued by relevant government agencies.
Investigation Highlights Growing Cybersecurity Risks
The alleged fraud demonstrates how weaknesses in financial technology infrastructure can expose lenders to substantial losses. It also highlights the need to protect not only customer accounts but the internal systems that approve and transfer money.
As investigators continue tracing the stolen funds and examining the role of AI-assisted tools, the case is likely to intensify pressure on NBFCs to improve their security arrangements.
For the financial sector, the central challenge is to ensure that automated lending and payment systems remain efficient without allowing criminals to exploit trusted connections and software vulnerabilities to divert money.
WeeklyHunt editorial note: This is independent editorial coverage verified by our journalism desk.